Which type of pentest is right for your business? A guide to penetration testing strategies
NaunetOctober 1, 2026
A penetration test, or pentest, is an authorized, controlled security assessment designed to simulate a real-world cyberattack. Its purpose is not simply to produce a list of vulnerabilities, but to demonstrate the potential business impact of a successful attack and reveal the paths an attacker could take to reach an organization’s most valuable data or critical systems. The size of the industry reflects its growing importance: the global penetration testing market was valued at $1.7 billion in 2024 and is projected to reach $3.9 billion by 2029, representing a compound annual growth rate of 17.1%. The most appropriate penetration testing strategy depends on the purpose of the assessment.
What will you learn from this article?
-
Why automated vulnerability scanning is not enough on its own, and what additional value a penetration test provides.
-
The differences between three common approaches: compliance-driven pentesting, Penetration Testing as a Service (PTaaS), and Threat-Led Penetration Testing (TLPT).
-
When each approach is appropriate, which business situations it is best suited to, and why the three approaches are not mutually exclusive.
-
What a collaborative testing model tailored to the client’s specific needs looks like in practice.
Why is automated vulnerability scanning no longer enough?
An automated vulnerability scanner can check a system against thousands of known vulnerability patterns in a matter of minutes and produce a clearly structured list of findings. Some scanners also perform safe validation checks, but their primary purpose is to identify known vulnerabilities automatically. Not to determine whether they can be exploited in practice or assess the resulting business risk.
A penetration test, by contrast, goes further. Within the agreed scope and rules of engagement, it determines whether a vulnerability is genuinely exploitable and whether it can be chained with other weaknesses that may appear insignificant in isolation.
Human expertise is particularly valuable when it comes to uncovering business logic flaws and multi-stage attack paths. A configuration issue that appears to pose little risk on its own can lead to a serious access control vulnerability when combined with a seemingly minor permissions issue. Automated tools often fail to identify these connections or assess their significance in a business context.
What drives organizations to conduct a pentest?
In our experience, an organization’s need for penetration testing almost always stems from one of two factors. The first is an external requirement: an audit, a business partner, or a piece of legislation requires security testing to be carried out regularly.
One example is NIS2 (the Network and Information Security Directive 2, the EU’s cybersecurity directive), which requires organizations to regularly evaluate the effectiveness of their cybersecurity risk-management measures. Penetration testing can form part of this process, but the appropriate method and frequency should be determined based on the organization’s risks and the applicable national and sector-specific requirements. A similar principle applies to ISO 27001 and SOC 2.
The second factor is a genuine commitment to strengthening the organization’s security posture and addressing existing weaknesses. This is often prompted by lessons learned from an actual security incident or by a management decision to prevent problems rather than respond to them after the damage has been done.
These two drivers help determine which of the three common penetration testing approaches is most appropriate.
Three common penetration testing approaches for different business needs
It is important to clarify that the following three approaches do not represent equivalent categories and are not mutually exclusive.
-
Compliance-driven pentesting primarily describes the motivation and objective behind an assessment.
-
Penetration Testing as a Service (PTaaS) is a service delivery and collaboration model that defines how penetration testing is provided and managed.
-
Threat-Led Penetration Testing (TLPT) is a structured, regulated testing methodology guided by threat intelligence.
These categories can overlap. For example, an assessment delivered through a PTaaS model may also be compliance-driven. Similarly, a TLPT conducted under DORA is both a threat-led methodology and a regulatory requirement.
We explored these three approaches in our article Choosing the Right Type of Penetration Test. Here, we compare them across a broader range of criteria to help decision-makers identify the approach best suited to their organization’s needs.
Compliance-driven pentesting
This is the most common entry point into penetration testing. The primary motivation is a legal, regulatory, contractual, or industry requirement, such as PCI DSS (Payment Card Industry Data Security Standard, which applies to systems that store, process, or transmit payment card data), ISO 27001, or SOC 2.
The assessment is conducted within the scope defined by the relevant framework. Its purpose is to demonstrate compliance and support a successful audit outcome, while helping the organization reduce its exposure to fines, legal risks, and reputational damage.
ISO/IEC 27001
control A.8.8 addresses the management of technical vulnerabilities, while A.8.29 covers security testing during development and acceptance. Penetration testing can support these controls and provide evidence that they are being implemented effectively, but the standard does not impose a universal requirement for annual testing. The appropriate frequency depends on the organization’s risk profile, existing controls, and contractual obligations.This approach is particularly well suited to organizations that handle sensitive data and are preparing for an audit, including fintech and healthcare companies. Its main limitation is that the scope may be narrower than the organization’s actual threat landscape. Passing an audit does not necessarily mean that a system can withstand a targeted, creative attack.
Continuous Penetration Testing as a Service (PTaaS)
Penetration Testing as a Service (PTaaS) emerged from the recognition that a once-a-year, point-in-time assessment cannot keep pace with a constantly evolving, DevOps-driven development environment.
The model provides continuous, platform-based feedback, offers actionable remediation guidance, and can scale effectively across fast-moving SaaS environments.
However, PTaaS also has its limitations. Some regulators may not accept it as sufficient evidence of compliance on its own, legal responsibilities and liabilities must be clearly defined, and the model cannot fully replace in-depth assessments involving complex, chained attack scenarios.
The PTaaS label alone does not guarantee the depth or quality of the assessment. Organizations should check whether the service includes manual testing, business logic testing, retesting, and access to expert consultation, or whether it primarily offers platform-based vulnerability management.
Threat-Led Penetration Testing (TLPT)
Threat-Led Penetration Testing (TLPT) is one of the most complex and tightly regulated forms of security testing. It assesses whether an organization could withstand a specific, real-world attack and therefore goes far beyond producing a simple list of vulnerabilities. The methodology is informed by real-world threat intelligence and the tactics, techniques, and procedures (TTPs) used by relevant threat actors.
In the EU, Article 26 of the Digital Operational Resilience Act (DORA) requires certain financial entities to conduct TLPT at least once every three years. This obligation does not automatically apply to every financial organization. The competent authorities identify the entities required to perform TLPT based on the criteria set out in the regulation.
The methodology is based on the TIBER-EU framework, developed by the European Central Bank to harmonize threat intelligence-led ethical red teaming across Europe. Under specified conditions and subject to approval by the competent authority, DORA also permits the use of internal testers rather than requiring organizations to rely exclusively on external, accredited experts.
Which pentest approach should you choose, and when?
| Criterion | Compliance-driven | PTaaS | TLPT |
|---|---|---|---|
| Primary objective | Meeting audit, regulatory, or contractual requirements | Receiving continuous security feedback | Assessing resilience against real-world threats |
| Typical client | Organizations that handle sensitive data and are preparing for an audit | Fast-moving SaaS and DevOps teams | Designated entities in the financial sector |
| Frequency | As required by the relevant standard, regulation, or contract | Continuous, without a fixed schedule | At least once every three years for in-scope entities |
| Main limitation | Potentially narrow scope and a risk of becoming a box-ticking exercise | May not be accepted as sufficient compliance evidence on its own | High resource and time requirements |
Common misconceptions about penetration testing
“A vulnerability scan and a penetration test are the same thing, just under different names.”
This is one of the most costly misconceptions, as it can lead an organization to rely on an automated tool to answer questions that require human judgment, creativity, and an understanding of business context.
“We are ISO 27001 certified, so we do not need any further security testing.”
Certification demonstrates that the organization has established and operates an information security management system, including processes for managing technical vulnerabilities. However, it does not prove that a targeted, creative attacker would be unable to compromise its systems. Certification and real-world resilience are distinct, though closely related, and neither can replace the other.
“PTaaS completely replaces traditional, in-depth penetration testing.”
A continuous, platform-based model provides faster feedback and is well suited to constantly evolving development environments. However, PTaaS alone may not be sufficient when the objective is to uncover a complex attack scenario spanning multiple systems and involving human factors, or when strict regulatory requirements (such as TLPT) call for an in-depth, threat-led assessment.
The two models are therefore complementary rather than interchangeable: PTaaS provides continuous baseline coverage, while deeper, periodic assessments focus on critical and complex risks.
How Naunet works: A collaborative approach
A common limitation of off-the-shelf penetration tests is their narrow scope and the fact that they provide only a single point-in-time view of a system’s security. For smaller systems with a stable scope, this may be sufficient, and even more practical than a broader, ongoing engagement.
At Naunet, every engagement begins with a comprehensive review of the client’s infrastructure and architecture, conducted in close collaboration with the client to identify risks specific to their environment. We do not simply work through a generic checklist. If technical constraints exist in the development or UAT environment (for example, if VPN access is unavailable), we adapt the testing focus and methodology accordingly. During the collaborative scoping phase, we identify and prioritize the areas that matter most.
Our team has completed more than 70 projects to date, including over 40 penetration tests and more than six red team exercises. This experience underpins a proven, repeatable approach that we apply in our day-to-day work.
At the end of the engagement, the client receives far more than a list of vulnerabilities. The report includes an executive summary that translates the findings into business risk, along with detailed technical findings, CVSS scores (Common Vulnerability Scoring System, the standardized scale used to rate vulnerability severity from 0 to 10), and clear steps to reproduce each issue. This is followed by a remediation roadmap that prioritizes corrective actions and a retest that closes the testing cycle.
This model is particularly well suited to organizations where:
-
a security incident has already occurred,
-
the system changes frequently as new modules are introduced,
-
the organization has a custom or complex architecture,
-
regular security feedback is required.
What can delayed security testing cost a business?
According to IBM’s 2026 Cost of a Data Breach Report, the global average cost of a data breach reached $4.99 million, up 12% from the previous year. One in four malicious breaches was AI-enabled, a 56% increase over the previous year, and AI-enabled breaches cost an average of approximately $6 million.
These figures illustrate the potential financial impact of cybersecurity risk on businesses. Choosing the right testing strategy can form an important part of a broader risk management framework.
There is no one-size-fits-all approach
Which type of penetration test is right for an organization depends on what the assessment is intended to achieve: meeting audit requirements, keeping pace with an evolving system, or demonstrating resilience against real-world threats. The key is to work with a partner who understands how the organization operates and can translate technical findings into meaningful business context.
Not sure which testing model is right for your systems? Request a free consultation, and together we will determine where compliance-driven, threat-led, or continuous penetration testing can deliver the greatest value.
Frequently asked questions about pentest
How long does a penetration test take?
The duration depends on the size and complexity of the scope, as well as the required depth of testing. A focused assessment of a single application may be completed within a few weeks, while a collaborative assessment covering an entire infrastructure will require more time and careful scheduling.
How much does a penetration test cost, and what determines the price?
The cost primarily depends on the scope, the chosen testing model, and the depth of the assessment. An accurate quote can only be provided once the scoping phase has been completed.
What is a retest, and why is it important?
A retest is a follow-up assessment of the implemented fixes. The tester revisits the vulnerabilities identified during the original assessment and verifies that the remediation has effectively eliminated the associated risk. The process is completed by a successful retest, not simply by delivering the report.
What is the difference between the NIS2 and DORA requirements?
NIS2 requires covered organizations to implement appropriate and proportionate cybersecurity risk-management measures and to assess their effectiveness. Penetration testing can form part of this process. DORA focuses specifically on digital operational resilience in the financial sector, but its TLPT requirement applies only to certain financial entities identified by the competent authorities. These entities must conduct Threat-Led Penetration Testing at least once every three years.
Explore the Latest in Cybersecurity
Stay ahead of cyber threats with insights from the Naunet blog. Our experts share their knowledge on the latest cyber defense trends, techniques, and technologies. Whether you want to deepen your understanding or apply new strategies, our blog is your go-to resource for reliable, expert-backed content in the cybersecurity domain. Join our community of professionals and elevate your security posture with every post.
How collaboration, AI-assisted testing and an architecture-first approach help align penetration tests with changing systems and business risks.
OpenClaw is an open source AI assistant that runs on your machine and connects to chat apps like Telegram, Discord, and Slack. It is useful because it collapses message intake, web access, tool invocation, and stored authority into one runtime. These features make it a very inviting application however that is also the core danger.
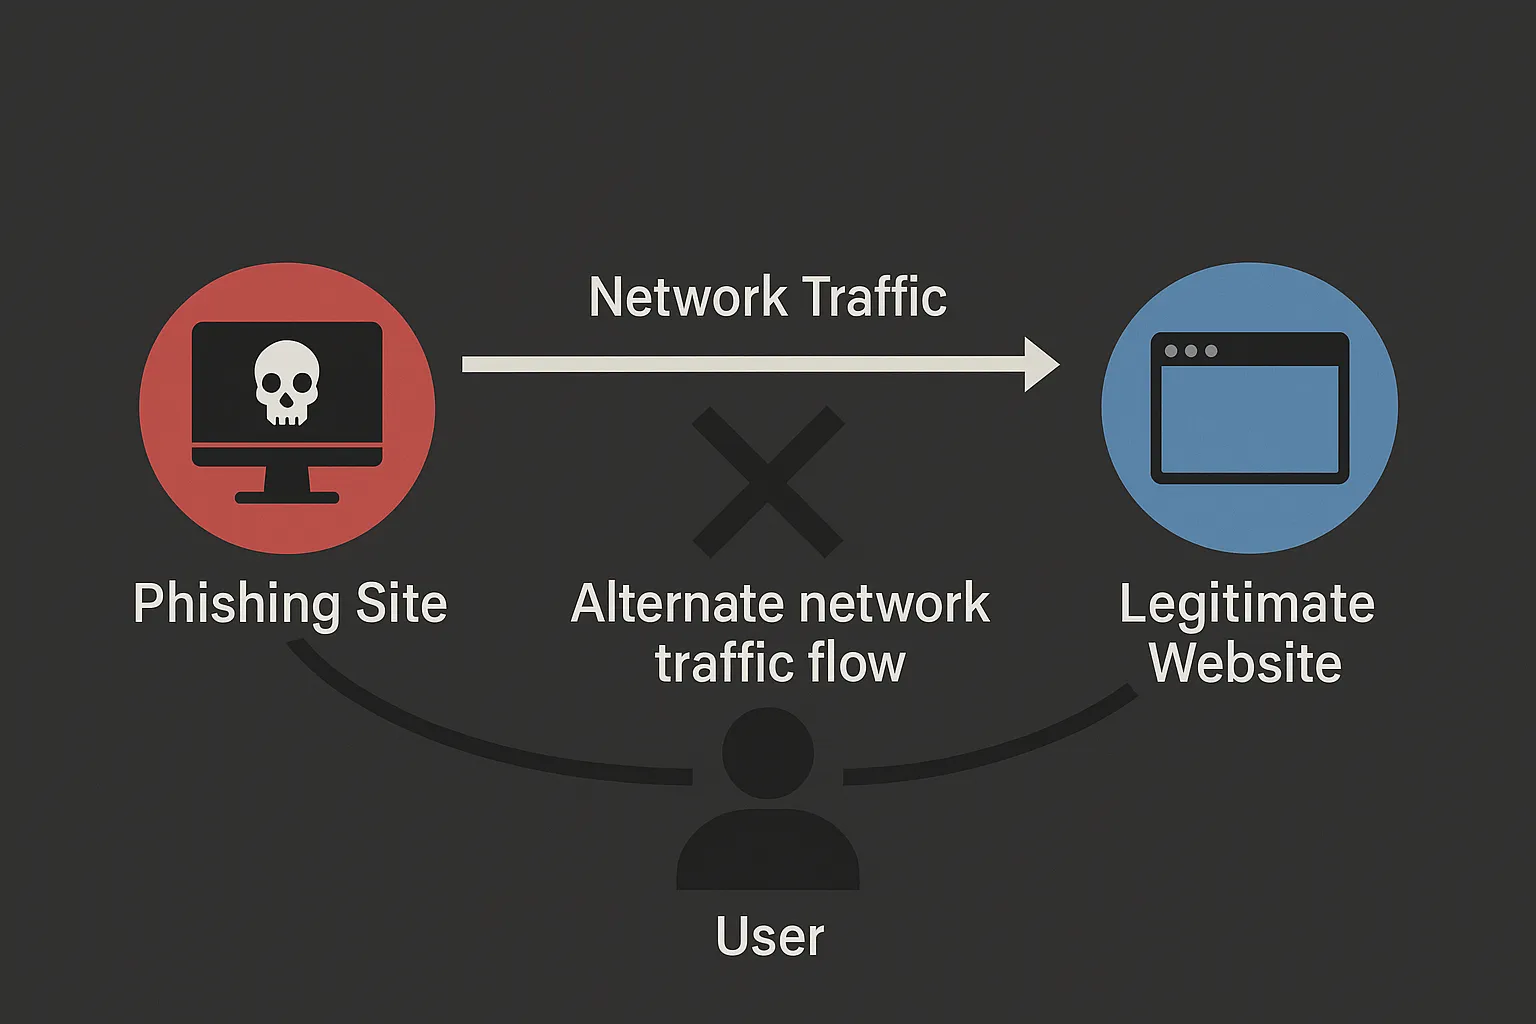
How to use Evilginx 3 with Custom Certificates
Two ways to use Evilginx 3 community edition with custom (even wildcard) certificates.
Last year, I conducted a phishing campaign as part of a red team assessment. Let me share what I learned about SPAM filters. I also had access to the internal mailing system, allowing me to test my theories on the target.
Stealthier than Nmap: ShadowProbe
ShadowProbe is a custom-made, TCP-only port scanner designed for multiple targets, featuring an inbuilt scheduler. It is a tool intended to run for days or even weeks once started.
LegolAD is an enumeration tool that allows configurable network traffic for LDAP requests in Active Directory. It can be configured for scope, pagination, and jitter. The idea behind it was to evade detection by custom monitoring systems.